Arquitectura
Ubicación en los nodos
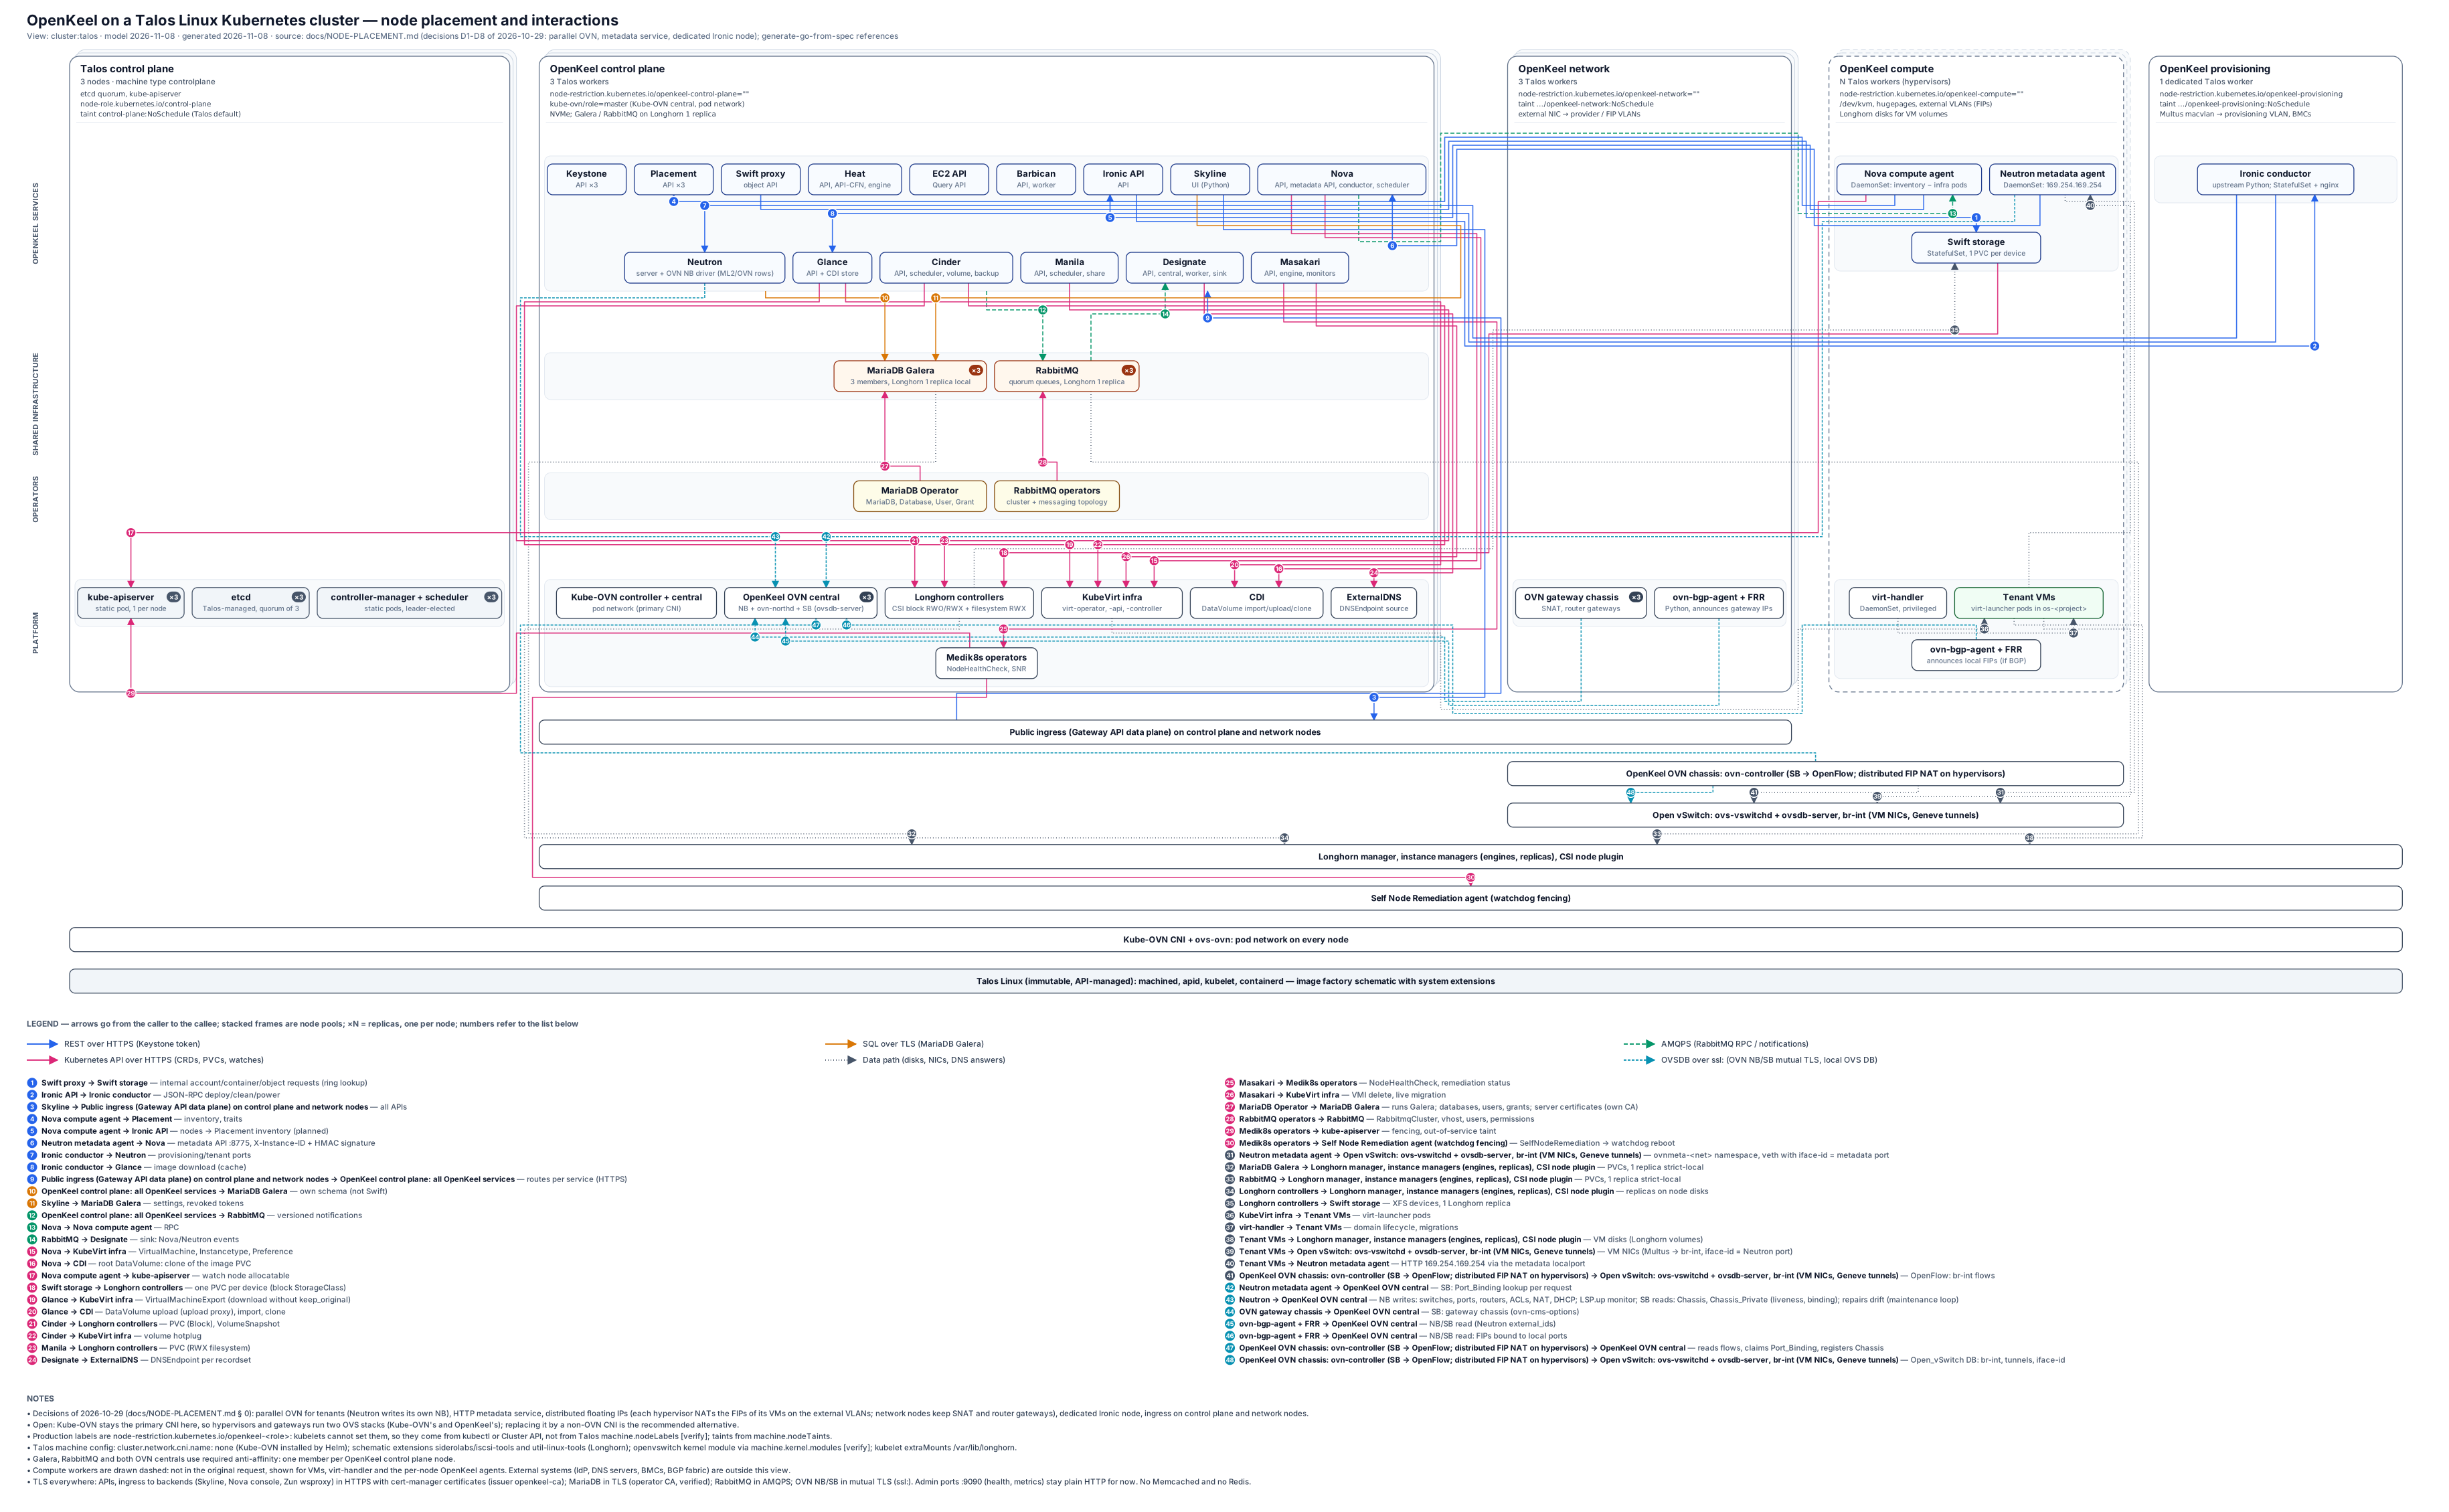
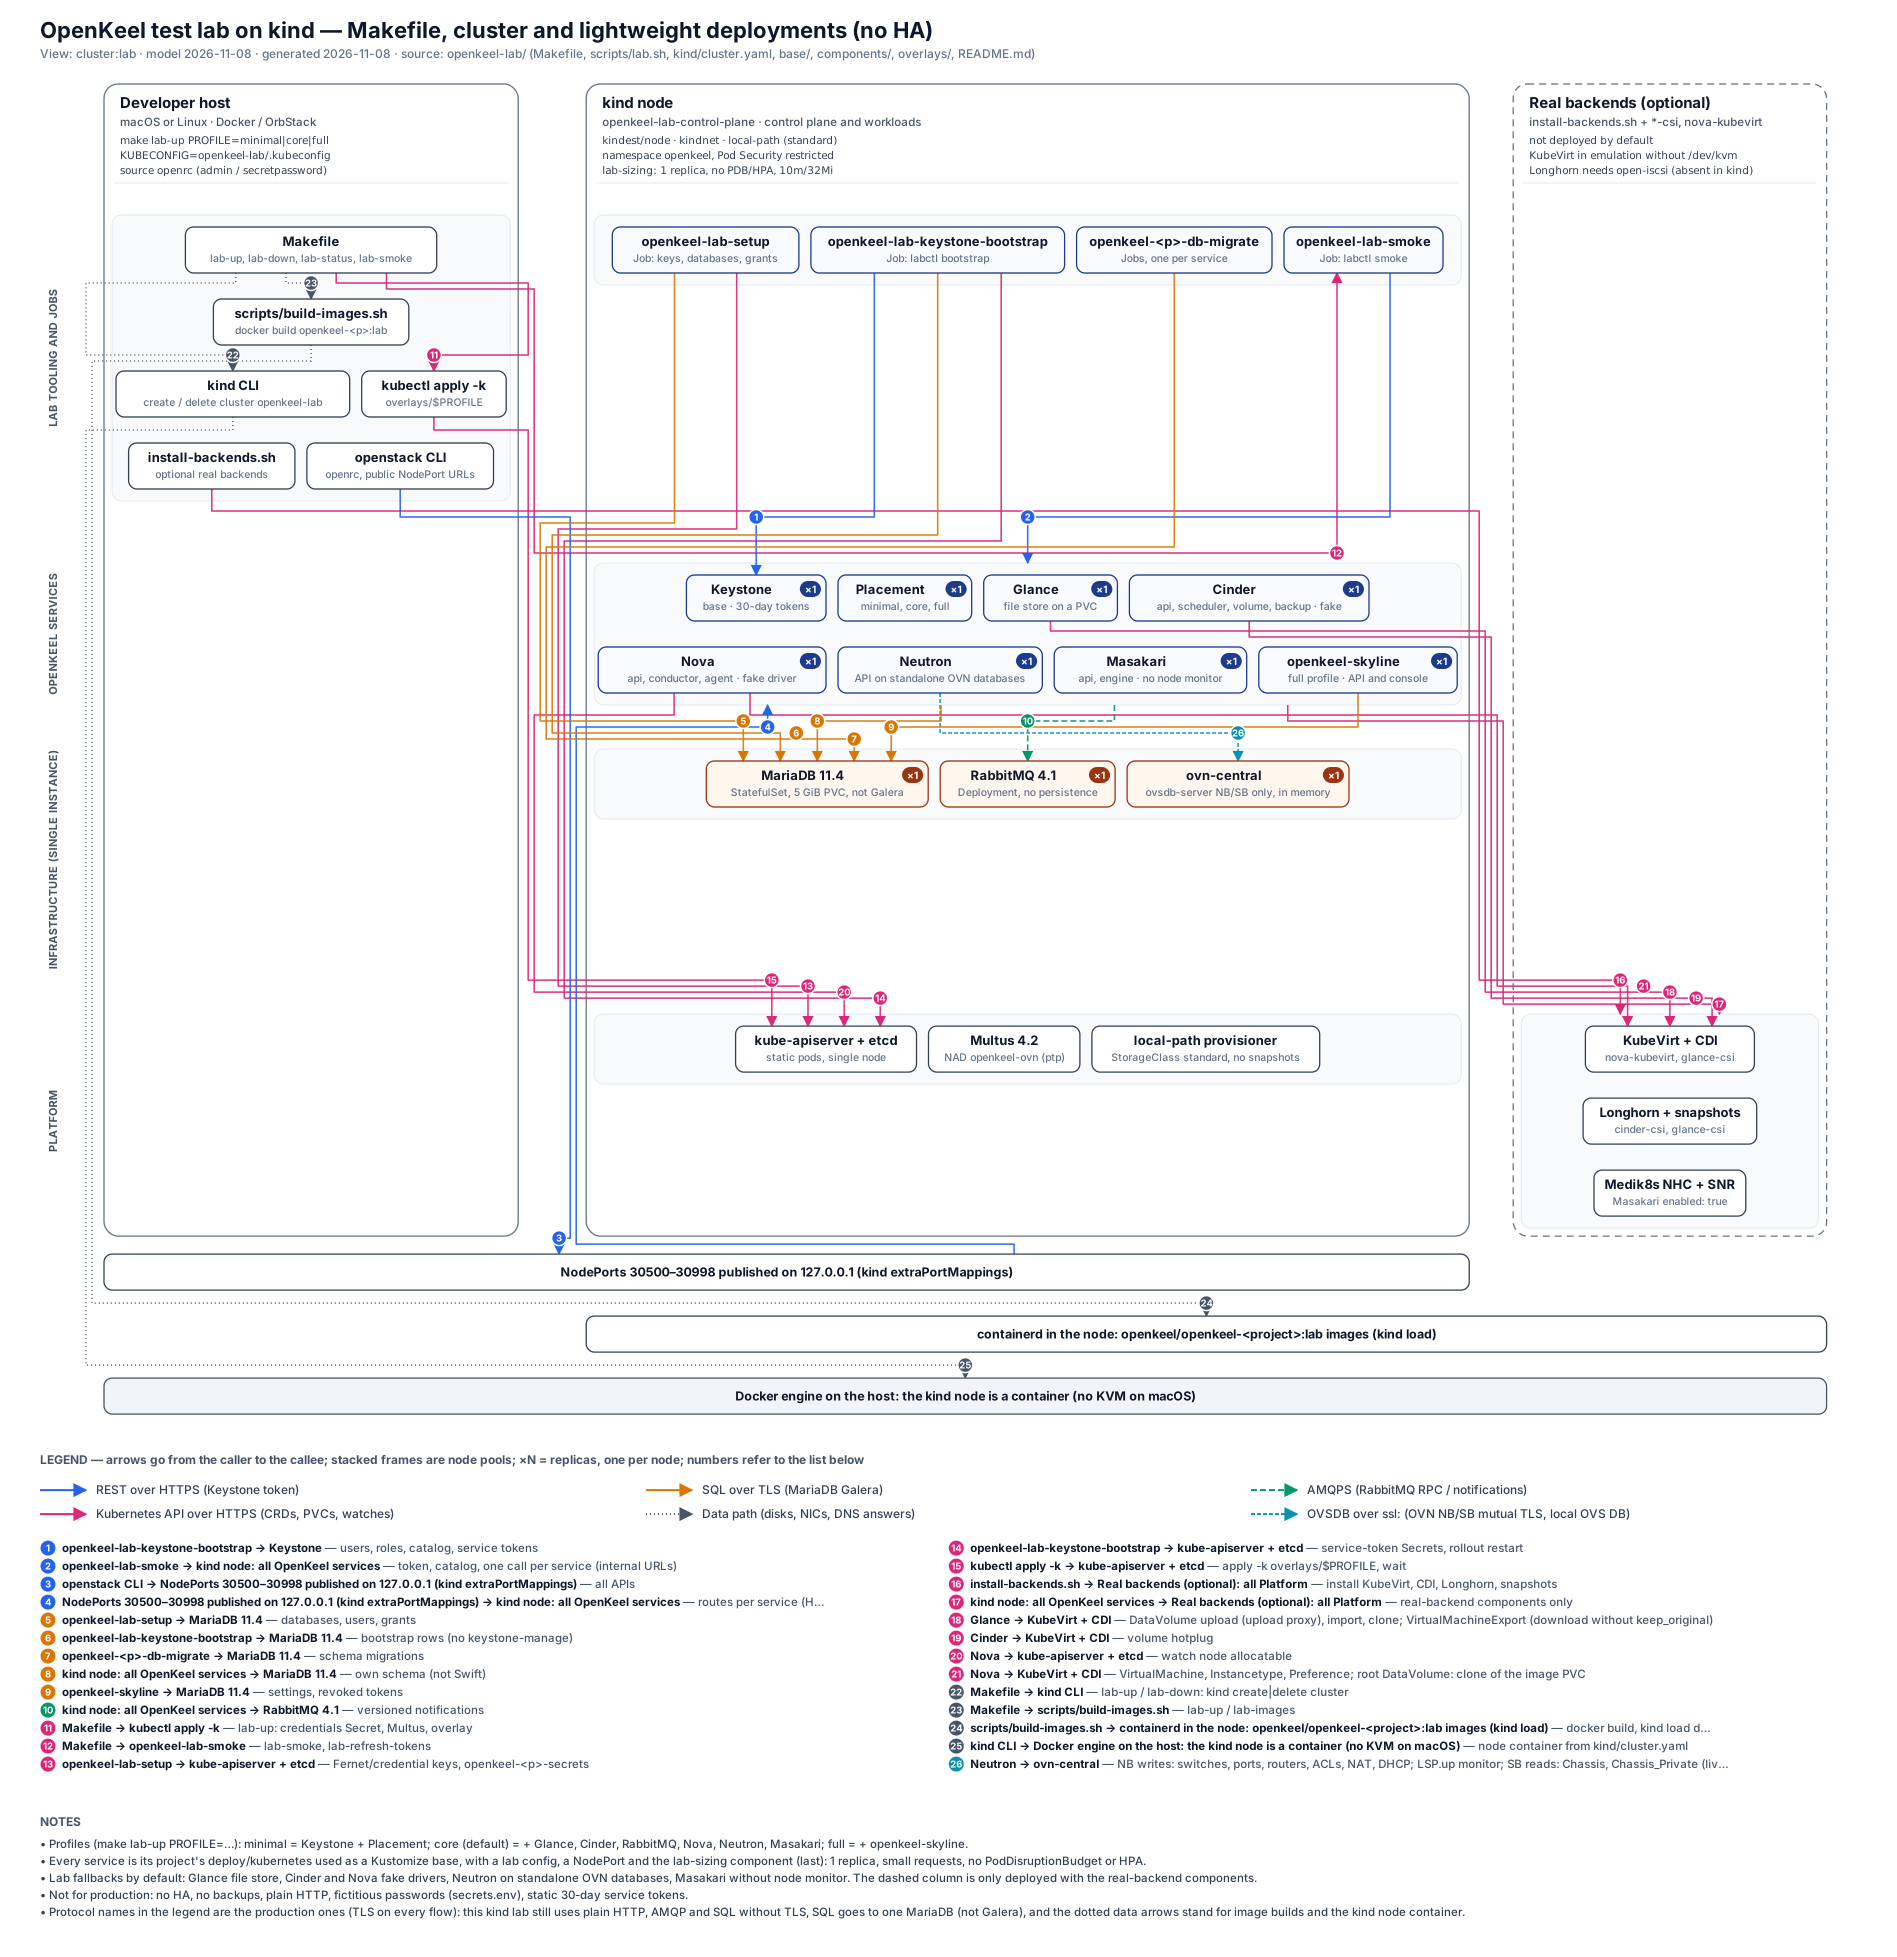
Dónde se ejecuta cada componente: el clúster de producción Talos y el laboratorio ligero kind.
Clúster de producción Talos
 Pantalla completa
Leyenda y detalles
OpenKeel interactions — view cluster:talos
| # | From | To | Protocol | What |
|---|---|---|---|---|
| 1 | Swift proxy | Swift storage | REST over HTTPS (Keystone token) | internal account/container/object requests (ring lookup) |
| 2 | Ironic API | Ironic conductor | REST over HTTPS (Keystone token) | JSON-RPC deploy/clean/power |
| 3 | Skyline | Public ingress (Gateway API data plane) on control plane and network nodes | REST over HTTPS (Keystone token) | all APIs |
| 4 | Nova compute agent | Placement | REST over HTTPS (Keystone token) | inventory, traits |
| 5 | Nova compute agent | Ironic API | REST over HTTPS (Keystone token) | nodes → Placement inventory (planned) |
| 6 | Neutron metadata agent | Nova | REST over HTTPS (Keystone token) | metadata API :8775, X-Instance-ID + HMAC signature |
| 7 | Ironic conductor | Neutron | REST over HTTPS (Keystone token) | provisioning/tenant ports |
| 8 | Ironic conductor | Glance | REST over HTTPS (Keystone token) | image download (cache) |
| 9 | Public ingress (Gateway API data plane) on control plane and network nodes | OpenKeel control plane: all OpenKeel services | REST over HTTPS (Keystone token) | routes per service (HTTPS) |
| 10 | OpenKeel control plane: all OpenKeel services | MariaDB Galera | SQL over TLS (MariaDB Galera) | own schema (not Swift) |
| 11 | Skyline | MariaDB Galera | SQL over TLS (MariaDB Galera) | settings, revoked tokens |
| 12 | OpenKeel control plane: all OpenKeel services | RabbitMQ | AMQPS (RabbitMQ RPC / notifications) | versioned notifications |
| 13 | Nova | Nova compute agent | AMQPS (RabbitMQ RPC / notifications) | RPC |
| 14 | RabbitMQ | Designate | AMQPS (RabbitMQ RPC / notifications) | sink: Nova/Neutron events |
| 15 | Nova | KubeVirt infra | Kubernetes API over HTTPS (CRDs, PVCs, watches) | VirtualMachine, Instancetype, Preference |
| 16 | Nova | CDI | Kubernetes API over HTTPS (CRDs, PVCs, watches) | root DataVolume: clone of the image PVC |
| 17 | Nova compute agent | kube-apiserver | Kubernetes API over HTTPS (CRDs, PVCs, watches) | watch node allocatable |
| 18 | Swift storage | Longhorn controllers | Kubernetes API over HTTPS (CRDs, PVCs, watches) | one PVC per device (block StorageClass) |
| 19 | Glance | KubeVirt infra | Kubernetes API over HTTPS (CRDs, PVCs, watches) | VirtualMachineExport (download without keep_original) |
| 20 | Glance | CDI | Kubernetes API over HTTPS (CRDs, PVCs, watches) | DataVolume upload (upload proxy), import, clone |
| 21 | Cinder | Longhorn controllers | Kubernetes API over HTTPS (CRDs, PVCs, watches) | PVC (Block), VolumeSnapshot |
| 22 | Cinder | KubeVirt infra | Kubernetes API over HTTPS (CRDs, PVCs, watches) | volume hotplug |
| 23 | Manila | Longhorn controllers | Kubernetes API over HTTPS (CRDs, PVCs, watches) | PVC (RWX filesystem) |
| 24 | Designate | ExternalDNS | Kubernetes API over HTTPS (CRDs, PVCs, watches) | DNSEndpoint per recordset |
| 25 | Masakari | Medik8s operators | Kubernetes API over HTTPS (CRDs, PVCs, watches) | NodeHealthCheck, remediation status |
| 26 | Masakari | KubeVirt infra | Kubernetes API over HTTPS (CRDs, PVCs, watches) | VMI delete, live migration |
| 27 | MariaDB Operator | MariaDB Galera | Kubernetes API over HTTPS (CRDs, PVCs, watches) | runs Galera; databases, users, grants; server certificates (own CA) |
| 28 | RabbitMQ operators | RabbitMQ | Kubernetes API over HTTPS (CRDs, PVCs, watches) | RabbitmqCluster, vhost, users, permissions |
| 29 | Medik8s operators | kube-apiserver | Kubernetes API over HTTPS (CRDs, PVCs, watches) | fencing, out-of-service taint |
| 30 | Medik8s operators | Self Node Remediation agent (watchdog fencing) | Kubernetes API over HTTPS (CRDs, PVCs, watches) | SelfNodeRemediation → watchdog reboot |
| 31 | Neutron metadata agent | Open vSwitch: ovs-vswitchd + ovsdb-server, br-int (VM NICs, Geneve tunnels) | Data path (disks, NICs, DNS answers) | ovnmeta-<net> namespace, veth with iface-id = metadata port |
| 32 | MariaDB Galera | Longhorn manager, instance managers (engines, replicas), CSI node plugin | Data path (disks, NICs, DNS answers) | PVCs, 1 replica strict-local |
| 33 | RabbitMQ | Longhorn manager, instance managers (engines, replicas), CSI node plugin | Data path (disks, NICs, DNS answers) | PVCs, 1 replica strict-local |
| 34 | Longhorn controllers | Longhorn manager, instance managers (engines, replicas), CSI node plugin | Data path (disks, NICs, DNS answers) | replicas on node disks |
| 35 | Longhorn controllers | Swift storage | Data path (disks, NICs, DNS answers) | XFS devices, 1 Longhorn replica |
| 36 | KubeVirt infra | Tenant VMs | Data path (disks, NICs, DNS answers) | virt-launcher pods |
| 37 | virt-handler | Tenant VMs | Data path (disks, NICs, DNS answers) | domain lifecycle, migrations |
| 38 | Tenant VMs | Longhorn manager, instance managers (engines, replicas), CSI node plugin | Data path (disks, NICs, DNS answers) | VM disks (Longhorn volumes) |
| 39 | Tenant VMs | Open vSwitch: ovs-vswitchd + ovsdb-server, br-int (VM NICs, Geneve tunnels) | Data path (disks, NICs, DNS answers) | VM NICs (Multus → br-int, iface-id = Neutron port) |
| 40 | Tenant VMs | Neutron metadata agent | Data path (disks, NICs, DNS answers) | HTTP 169.254.169.254 via the metadata localport |
| 41 | OpenKeel OVN chassis: ovn-controller (SB → OpenFlow; distributed FIP NAT on hypervisors) | Open vSwitch: ovs-vswitchd + ovsdb-server, br-int (VM NICs, Geneve tunnels) | Data path (disks, NICs, DNS answers) | OpenFlow: br-int flows |
| 42 | Neutron metadata agent | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | SB: Port_Binding lookup per request |
| 43 | Neutron | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | NB writes: switches, ports, routers, ACLs, NAT, DHCP; LSP.up monitor; SB reads: Chassis, Chassis_Private (liveness, binding); repairs drift (maintenance loop) |
| 44 | OVN gateway chassis | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | SB: gateway chassis (ovn-cms-options) |
| 45 | ovn-bgp-agent + FRR | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | NB/SB read (Neutron external_ids) |
| 46 | ovn-bgp-agent + FRR | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | NB/SB read: FIPs bound to local ports |
| 47 | OpenKeel OVN chassis: ovn-controller (SB → OpenFlow; distributed FIP NAT on hypervisors) | OpenKeel OVN central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | reads flows, claims Port_Binding, registers Chassis |
| 48 | OpenKeel OVN chassis: ovn-controller (SB → OpenFlow; distributed FIP NAT on hypervisors) | Open vSwitch: ovs-vswitchd + ovsdb-server, br-int (VM NICs, Geneve tunnels) | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | Open_vSwitch DB: br-int, tunnels, iface-id |
laboratorio kind
 Pantalla completa
Leyenda y detalles
OpenKeel interactions — view cluster:lab
| # | From | To | Protocol | What | |
|---|---|---|---|---|---|
| 1 | openkeel-lab-keystone-bootstrap | Keystone | REST over HTTPS (Keystone token) | users, roles, catalog, service tokens | |
| 2 | openkeel-lab-smoke | kind node: all OpenKeel services | REST over HTTPS (Keystone token) | token, catalog, one call per service (internal URLs) | |
| 3 | openstack CLI | NodePorts 30500–30998 published on 127.0.0.1 (kind extraPortMappings) | REST over HTTPS (Keystone token) | all APIs | |
| 4 | NodePorts 30500–30998 published on 127.0.0.1 (kind extraPortMappings) | kind node: all OpenKeel services | REST over HTTPS (Keystone token) | routes per service (HTTPS) | |
| 5 | openkeel-lab-setup | MariaDB 11.4 | SQL over TLS (MariaDB Galera) | databases, users, grants | |
| 6 | openkeel-lab-keystone-bootstrap | MariaDB 11.4 | SQL over TLS (MariaDB Galera) | bootstrap rows (no keystone-manage) | |
| 7 | openkeel-<p>-db-migrate | MariaDB 11.4 | SQL over TLS (MariaDB Galera) | schema migrations | |
| 8 | kind node: all OpenKeel services | MariaDB 11.4 | SQL over TLS (MariaDB Galera) | own schema (not Swift) | |
| 9 | openkeel-skyline | MariaDB 11.4 | SQL over TLS (MariaDB Galera) | settings, revoked tokens | |
| 10 | kind node: all OpenKeel services | RabbitMQ 4.1 | AMQPS (RabbitMQ RPC / notifications) | versioned notifications | |
| 11 | Makefile | kubectl apply -k | Kubernetes API over HTTPS (CRDs, PVCs, watches) | lab-up: credentials Secret, Multus, overlay | |
| 12 | Makefile | openkeel-lab-smoke | Kubernetes API over HTTPS (CRDs, PVCs, watches) | lab-smoke, lab-refresh-tokens | |
| 13 | openkeel-lab-setup | kube-apiserver + etcd | Kubernetes API over HTTPS (CRDs, PVCs, watches) | Fernet/credential keys, openkeel-<p>-secrets | |
| 14 | openkeel-lab-keystone-bootstrap | kube-apiserver + etcd | Kubernetes API over HTTPS (CRDs, PVCs, watches) | service-token Secrets, rollout restart | |
| 15 | kubectl apply -k | kube-apiserver + etcd | Kubernetes API over HTTPS (CRDs, PVCs, watches) | apply -k overlays/$PROFILE, wait | |
| 16 | install-backends.sh | Real backends (optional): all Platform | Kubernetes API over HTTPS (CRDs, PVCs, watches) | install KubeVirt, CDI, Longhorn, snapshots | |
| 17 | kind node: all OpenKeel services | Real backends (optional): all Platform | Kubernetes API over HTTPS (CRDs, PVCs, watches) | real-backend components only | |
| 18 | Glance | KubeVirt + CDI | Kubernetes API over HTTPS (CRDs, PVCs, watches) | DataVolume upload (upload proxy), import, clone; VirtualMachineExport (download without keep_original) | |
| 19 | Cinder | KubeVirt + CDI | Kubernetes API over HTTPS (CRDs, PVCs, watches) | volume hotplug | |
| 20 | Nova | kube-apiserver + etcd | Kubernetes API over HTTPS (CRDs, PVCs, watches) | watch node allocatable | |
| 21 | Nova | KubeVirt + CDI | Kubernetes API over HTTPS (CRDs, PVCs, watches) | VirtualMachine, Instancetype, Preference; root DataVolume: clone of the image PVC | |
| 22 | Makefile | kind CLI | Data path (disks, NICs, DNS answers) | lab-up / lab-down: kind create | delete cluster |
| 23 | Makefile | scripts/build-images.sh | Data path (disks, NICs, DNS answers) | lab-up / lab-images | |
| 24 | scripts/build-images.sh | containerd in the node: openkeel/openkeel-<project>:lab images (kind load) | Data path (disks, NICs, DNS answers) | docker build, kind load docker-image | |
| 25 | kind CLI | Docker engine on the host: the kind node is a container (no KVM on macOS) | Data path (disks, NICs, DNS answers) | node container from kind/cluster.yaml | |
| 26 | Neutron | ovn-central | OVSDB over ssl: (OVN NB/SB mutual TLS, local OVS DB) | NB writes: switches, ports, routers, ACLs, NAT, DHCP; LSP.up monitor; SB reads: Chassis, Chassis_Private (liveness, binding); repairs drift (maintenance loop) |