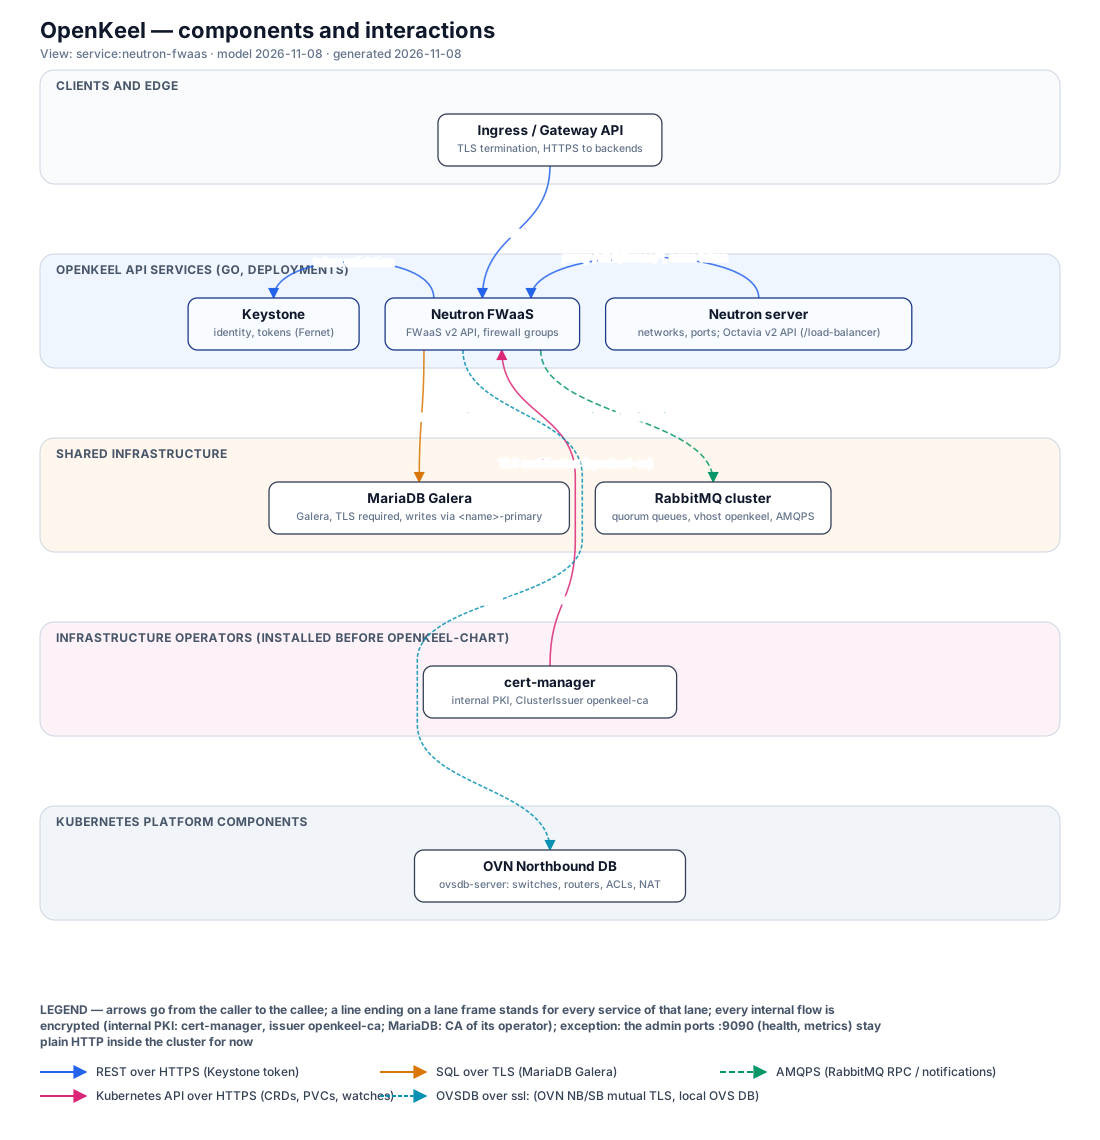
OpenKeel implementation in Go of OpenStack neutron-fwaas (neutron-fwaas-api), generated from the reverse-specification of branch stable/2026.2 by the generate-go-from-spec skill. It serves the FWaaS v2 API (/v2.0/fwaas) and programs firewall groups as OVN Port_Groups and stateless ACLs, replacing the firewall_v2 service plugin and its OVN driver: same routes, status codes, error bodies and policies, same NB rows. It runs beside openkeel-neutron, on its database and its OVN; clients reach it through a proxy in openkeel-neutron: see docs/NEUTRON-INTEGRATION.md. What is reproduced and what differs is in docs/CONFORMANCE.md; the security checklist is in docs/SECURITY.md.
Go module: github.com/openkeel/openkeel-neutron-fwaas
Binary: neutron-fwaas-api (API on port 9696, health and metrics on 9090)
Configuration: YAML, see config/config.example.yaml
Setting up a development environment, the database and the tests: docs/GETTING-STARTED.md
Database schema, migrations and upgrades: docs/DATABASE.md
Excerpt from openkeel-neutron-fwaas/README.md (in English).
REST API
23 operations of the original REST API (routes and body actions), and their state in OpenKeel.
Re-recorded Python FWaaS tests are replayed against the Go service, and the OVN driver is compared step by step with the real Python driver on a real Northbound.
Replay of recorded exchanges
E2E replay of re-recorded tests
691 exchanges of 135 Python tests, re-recorded with each request's identity, give the same answers.
How it runs
make e2e-strict, on go-mysql-server and on MariaDB 11.4.
Latest result 689 / 691 (2026-10-31); the 2 differences are a path outside the extension, 404 in both.
FWaaS v2 keeps its API on the OVN driver only, so the agent path with iptables, conntrack and NFLOG, the plugin loader and the manual sync tool are gone.
Done by the Cloud Native platform
Agent driver, iptables, conntrack and NFLOG
Taken over by OVN
Why it was left out
Firewall rules are OVN ACLs and Port_Groups written by the service; the L2 and L3 agent extensions and their RPC topics are not needed on OVN.
Why the solution is not affected
Firewall groups apply to router ports as on Python's OVN driver; VM ports are refused (409) there too. NFLOG network logging is not available.