Nova → KubeVirt
Instances are VirtualMachines; CDI imports the images
Learn moreOpenKeel: the sovereign French Cloud solution of the inherent group, with a European reach Discover inherent
Architecture
Clients, Go APIs, workers and agents, shared infrastructure, operators, the Kubernetes platform and external systems.
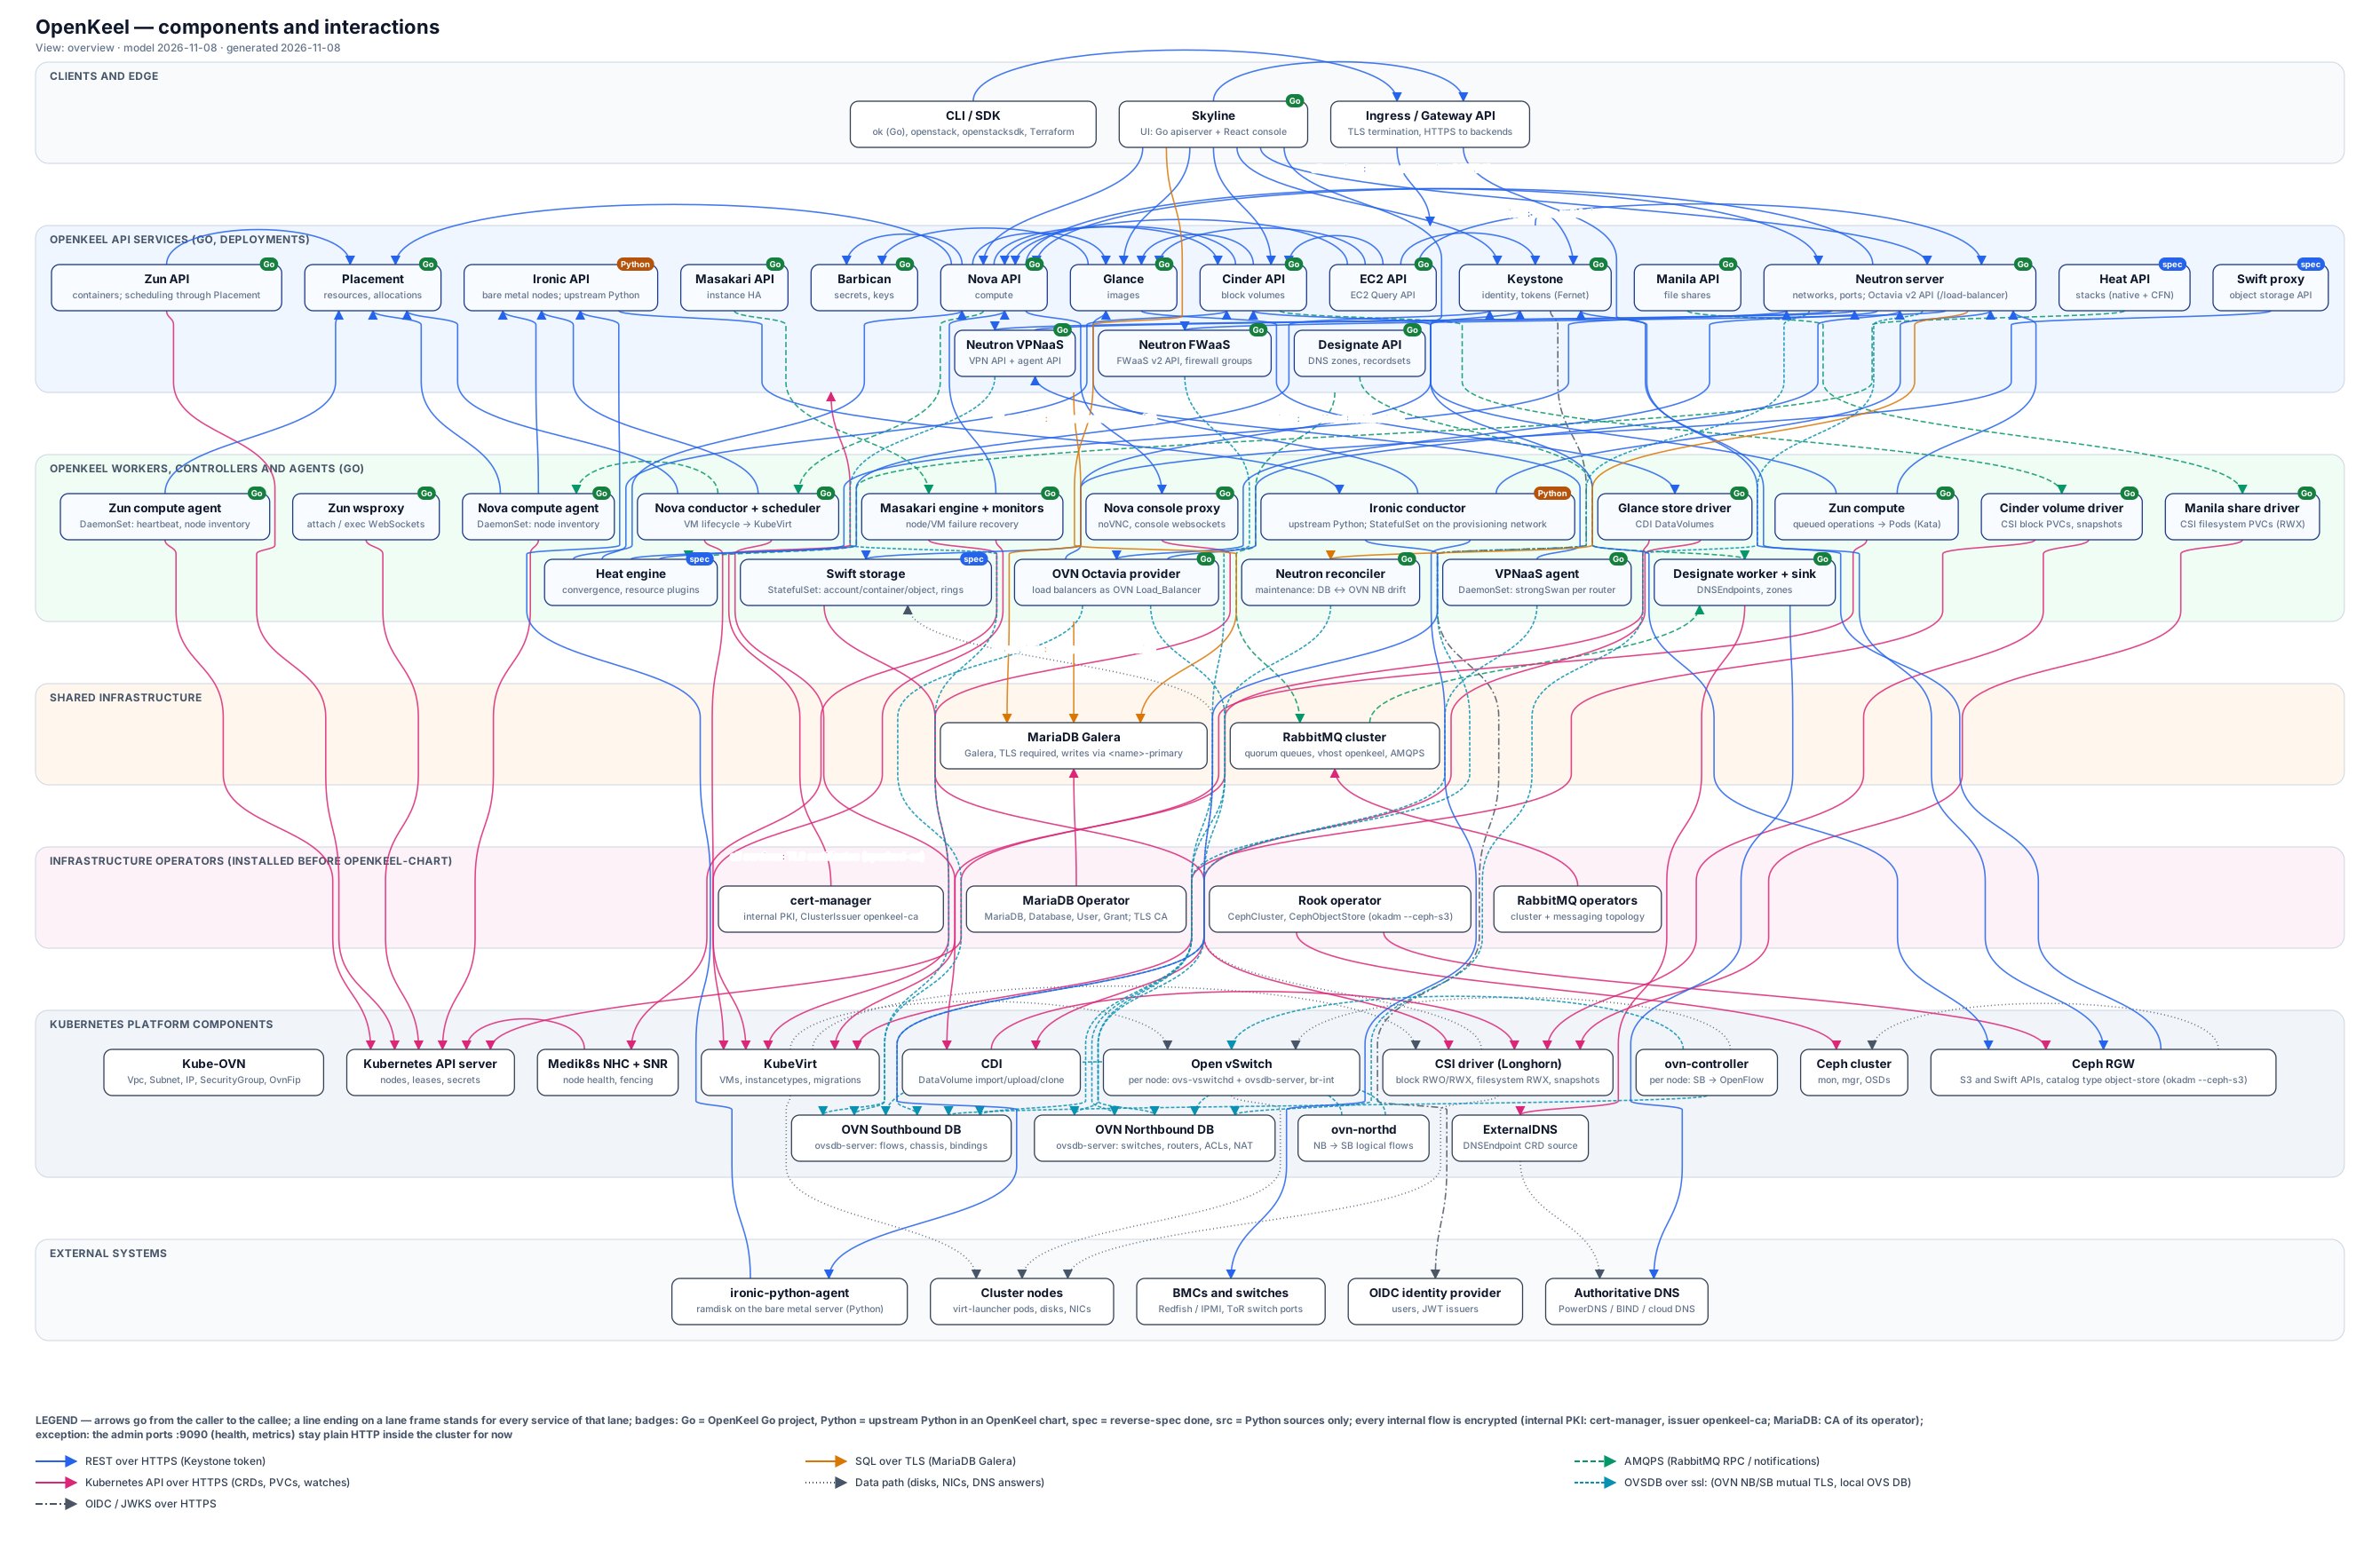 Full screen
Each service relies on a proven Kubernetes building block; Ironic is the exception, upstream Python in an OpenKeel chart.
Instances are VirtualMachines; CDI imports the images
Learn moreVolumes are PVCs on any block CSI: Rook-Ceph, Longhorn, NetApp, Dorado, Pure
Learn moreNFS gateway created on demand in the tenant network, on a block CSI volume
Learn moreVM network isolated from the Kubernetes network (Multus)
Learn moreRook-Ceph and its RGW gateway
Learn moreZones and records published by ExternalDNS
Learn moreNode Healthcheck and Self Node Remediation
Learn moreToo many hardware configurations to test
Learn moreA VM has no interface on the Kubernetes CNI network: each NIC is plugged into its own Neutron port in OpenKeel's OVN. A guard installed by the CNI plugin closes the paths through the namespaces it shares.
| Path | Why it is closed |
|---|---|
| Guest to another tenant network | The tap's only exit is the in-Pod bridge and the veth to br-int; ovn-controller maps it to one logical port. Other switches are reachable only through a Neutron router |
| Guest to the Pod network, the node, cluster Services | No interface of the guest touches them, and the guard closes the way through the shared namespaces |
| Spoofed MAC or IP | port_security of the logical port, written by Neutron |
| Another project's port | A project can create neither Pods nor NADs; only the service role can bind a port |
Source: openkeel-neutron/docs/VM-NETWORKING.md (§ Tenant isolation). make test-cni replays the attack in real namespaces, with and without the guard.