OpenKeel: the sovereign French Cloud solution of the inherent group, with a European reach Discover inherent

Components · Networking

Neutron-VPNaaS

Site-to-site IPsec VPN: IKE, IPsec policies, connections.

Go IPsec agentopenkeel-neutron-vpnaas

The module

OpenKeel implementation in Go of OpenStack neutron-vpnaas on the OVN path, generated from the reverse-specification of branch stable/2026.2 by the generate-go-from-spec skill. neutron-vpnaas-api serves the VPN API (/v2.0/vpn and the agent scheduler) and replaces the ovn-vpnaas service plugin and its driver: same routes, status codes, error bodies and policies, same tables. neutron-vpnaas-agent replaces neutron-ovn-vpn-agent: it runs strongSwan, the original's daemon, in one qvpn-<router> namespace per router. It runs beside openkeel-neutron, on its database and its OVN; clients reach it through a proxy in openkeel-neutron: see docs/NEUTRON-INTEGRATION.md. What is reproduced and what differs is in docs/CONFORMANCE.md; the security checklist is in docs/SECURITY.md.

  • Go module: github.com/openkeel/openkeel-neutron-vpnaas
  • Binaries: neutron-vpnaas-api (API on port 9696, agent API on 9697, health and metrics on 9090), neutron-vpnaas-agent (health on 9091; needs Linux, root and strongSwan: Dockerfile.agent)
  • Configuration: YAML, see config/config.example.yaml and config/agent.example.yaml
  • Setting up a development environment, the database and the tests: docs/GETTING-STARTED.md
  • Database schema, migrations and upgrades: docs/DATABASE.md

Excerpt from openkeel-neutron-vpnaas/README.md (in English).

REST API

35 operations of the original REST API (routes and body actions), and their state in OpenKeel.

  • 35Implemented

How compatibility is tested

Recorded exchanges of the OVN profile are replayed against the Go service, configuration rendering is compared with the original templates, and real IPsec tunnels are brought up end to end.

Replay of recorded exchanges

E2E replay of the OVN profile

The recorded VPNaaS exchanges served by this service give the same answers; those served by Neutron are checked on the real stack.

How it runs

make e2e-strict, on go-mysql-server and on MariaDB 11.4.

Latest result 84 replayed, 84 pass (2026-10-31); 25 of the 108 recorded exchanges belong to Neutron or no longer apply.
Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Unit and golden tests

Configuration rendering vectors

strongSwan configuration matches the original jinja2 templates for every group and algorithm of the API.

How it runs

tools/gen_render_vectors.py, 50 vectors from the original templates.

Latest result 50 / 50, blank lines aside (2026-10-31).

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Scenario

Real IPsec tunnel

IKEv1 and IKEv2 with AES-GCM, ping through ESP, admin down and up, a killed daemon restarted, removal.

How it runs

make tunnel-test: strongSwan 5.9.13 on both sides, real kernel XFRM.

Latest result Passes, 2 runs on the final code (2026-10-31).

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Scenario

Whole stack with Neutron and OVN

Through Neutron's proxy, a tenant port pings a subnet behind a strongSwan peer, via the OVN router and the tunnel.

How it runs

make stack-test: openkeel-neutron, ovsdb-server, ovn-northd, ovn-controller, OVS, MariaDB, the agent image.

Latest result Passes, 2 runs on the final code (2026-10-31).

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Concurrency on Galera

Concurrency on MariaDB Galera

VPN operations stay consistent when requests arrive through three Galera nodes.

How it runs

make galera-test on a 3-node cluster.

Latest result 3 tests pass, 5 runs out of 5 (2026-10-31).

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Tempest

neutron-tempest-plugin vpnaas

The upstream VPNaaS API and scenario tests.

How it runs

Needs a deployed cloud.

Latest result Not run.

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Left out of the rewrite

VPNaaS keeps its API with one strongSwan driver on OVN, without Libreswan, the legacy L3 path, rootwrap or RabbitMQ.

Obsolete or unused upstream

Libreswan driver and legacy L3-agent path

Why it was left out

They are not targets of the rewrite; one driver, strongSwan in a namespace per router on the OVN chassis, is shipped.

Why the solution is not affected

IPsec site connections are created through the same API; deployments that relied on Libreswan-specific behaviour do not get it.

Source: openkeel-neutron-vpnaas/config/dropped-options.md

Internal machinery simplified

RabbitMQ RPC and agent notifications

Why it was left out

The agent polls an agent API with ETag every 5 seconds instead of RPC topics; no OpenKeel service consumed the vpn_agent notifications.

Why the solution is not affected

A lost update cannot happen, at the cost of up to 5 s delay. The notifications become log lines.

Source: openkeel-neutron-vpnaas/docs/CONFORMANCE.md

Internal machinery simplified

rootwrap and interface drivers

Taken over by Kubernetes DaemonSet

Why it was left out

The agent drives OVS itself and runs with the privileges it needs in its container.

Why the solution is not affected

Same namespaces, ports and strongSwan commands on the node; no rootwrap filters to maintain.

Source: openkeel-neutron-vpnaas/config/dropped-options.md

Only what was left out by design is listed here; the work not done yet is in the Known gaps of the module's docs/CONFORMANCE.md. Every module

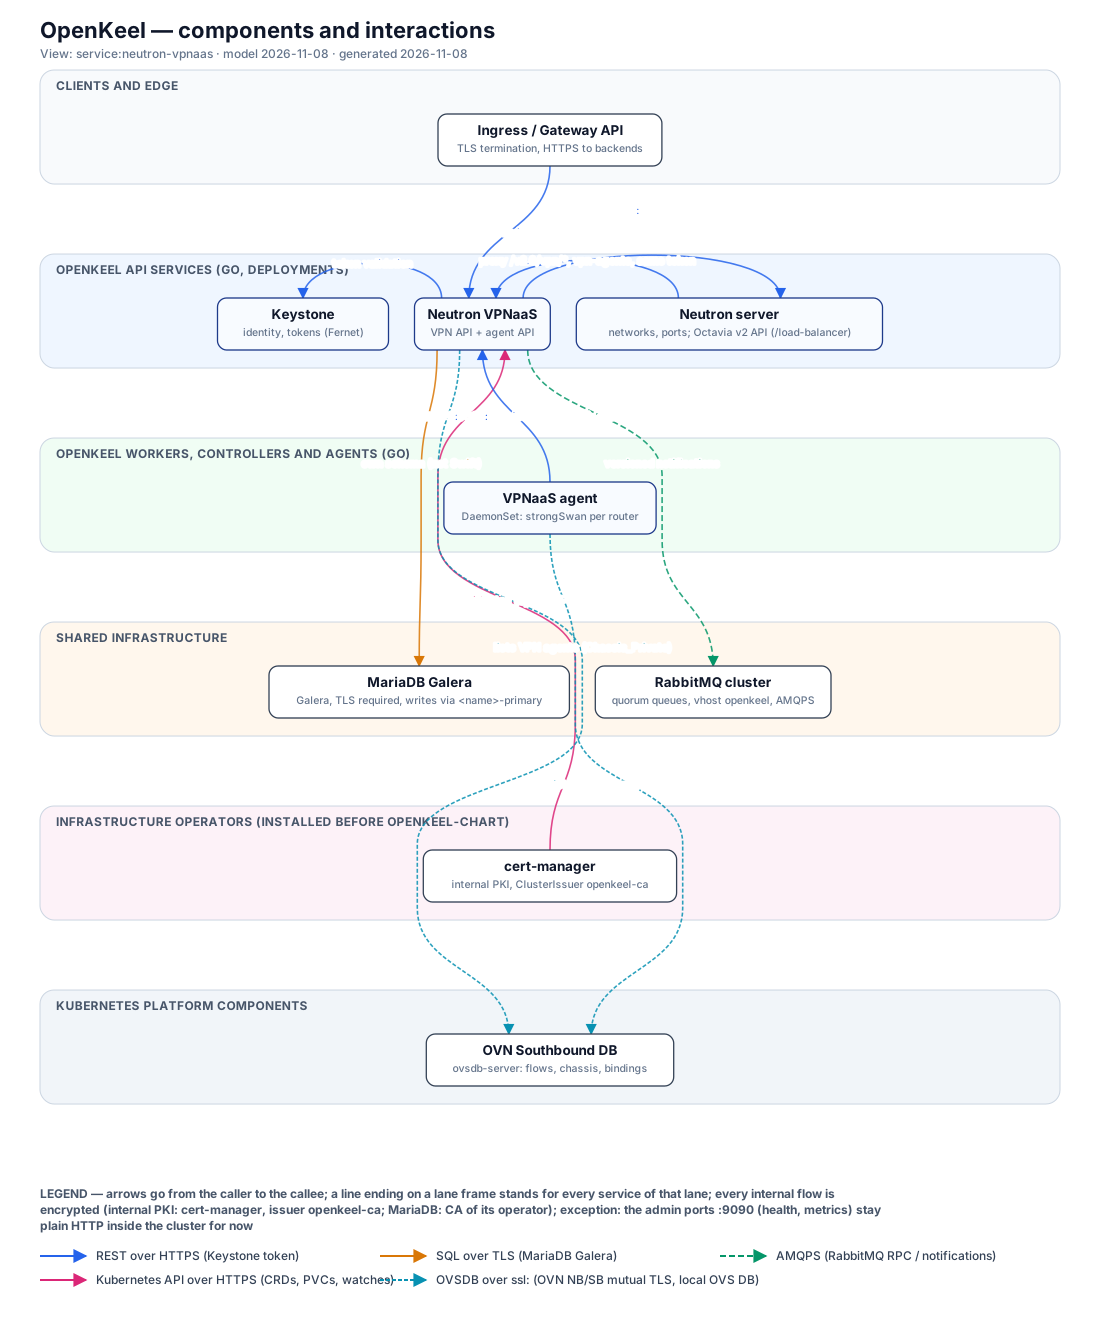
Neutron-VPNaaS interactions

Service view generated by the diagram skill from the OpenKeel model.

Diagram openkeel-neutron-vpnaas.svg Full screen
The 5 interactions of the model
FromToProtocolWhat
Neutron serverNeutron VPNaaSREST APIproxy /v2.0/vpn/*, vpn-agents, same token
Neutron VPNaaSNeutron serverREST APIcore and L3 calls: gateway ports, routes
Neutron VPNaaSOVN Southbound DBOVSDBlists VPN agents (Chassis_Private)
VPNaaS agentNeutron VPNaaSREST APIagent API :9697: services (ETag poll), status
VPNaaS agentOVN Southbound DBOVSDBregisters ovn-vpnagent, acks nb_cfg

Specifications